ClearSkies Identity Threat Protection
How ITP Decides
No individual signal is decisive on its own, and no individual signal can trigger an automated response by itself.
Six signal classes
Evaluated in parallel, no single signal decisive
One risk score
Weighted contributions, scored against the identity’s own baseline
Four risk bands
Thresholds and enforcement configured per tenant
Multi-signal verification
A single false-positive suspension on a business-critical identity erodes trust faster than ten correct detections build it. Accuracy is therefore not a quality attribute of an identity capability, it is the precondition for the capability being allowed to act at all.
ITP evaluates each identity event across independent detection sources in parallel and combines their weighted contributions into a single identity risk score.
Authentication anomaly
Impossible travel, a new device, off-hours access, scored against the per-identity baseline
Behavioral deviation
First-time access, volume and scope anomalies, against a learned baseline held separately for human and non-human identities
Privilege context
Escalation, shadow administrative rights and service-account misuse, weighted more heavily for elevated identities
Identity-attack signature
Spraying, Pass-the-Ticket, Kerberoasting and token theft, from a maintained library mapped to ATT&CK
Posture weakness
A dormant administrator, absent multi-factor authentication or a non-expiring password, which raises standing risk and lowers the threshold for scrutiny
Platform correlation
A compromised host, a blocked domain or an exposed credential, supplied by the engine
Risk bands and what the workflow does
False positives arise almost always the same way: a tool alerts on one weak signal, an off-hours login or a new location, without the context to know whether it means anything. Figure 1 shows how a verdict is reached instead.
| Risk band | What the workflow does |
|---|---|
| Critical | At Critical, automated containment is permitted, covering disable, session revocation and forced reset, an alert fires, and the event is sent to the engine. |
| High | At High, the finding is surfaced for immediate analyst action with one-click response available, and automated containment applies where tenant policy permits it. |
| Medium | At Medium, the finding is queued for triage, the identity is watched, and the event contributes to cumulative identity risk. |
| Low and informational | At Low and informational, the event is retained for baselining and traceability, and no enforcement follows. |
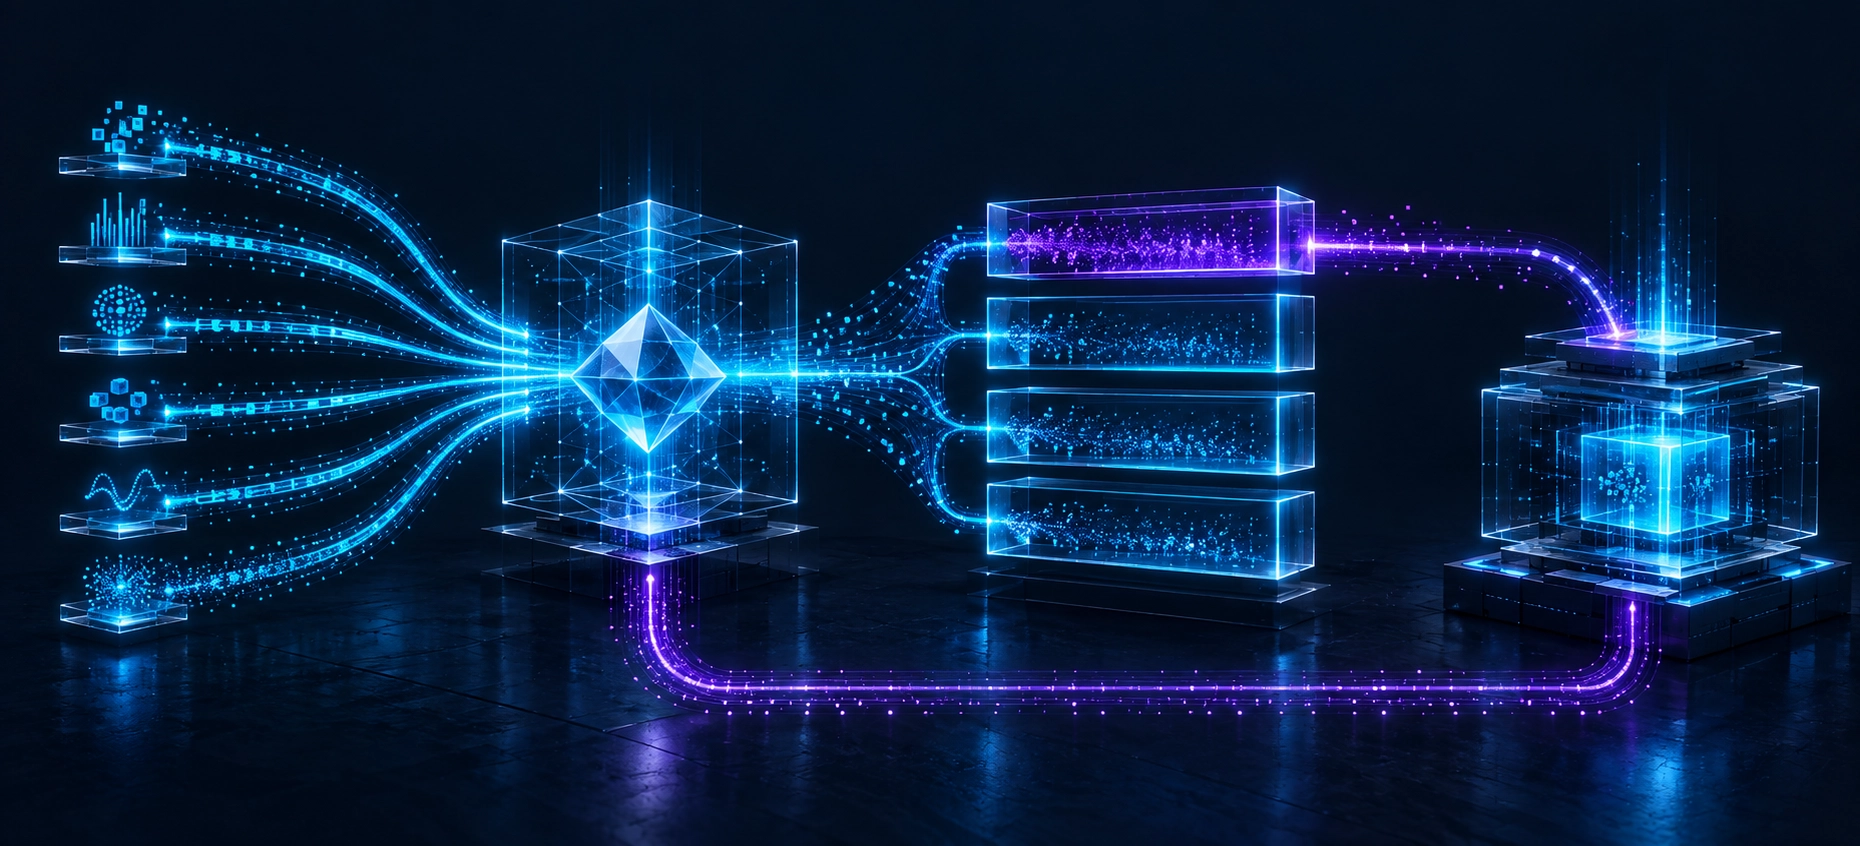
Figure 1. The signal classes, the risk bands, and the exchange with the TDIR engine.
Weighted scores map to bands, and the band determines what the workflow does rather than only how the finding is colored.
Band thresholds and the enforcement permitted at each band are configured per tenant, which is what allows one deployment to serve a regulated customer requiring analyst review of every action alongside a customer requiring containment without human latency.
Baselines retrain continuously against each tenant’s observed activity, and analyst verdicts feed back into them, so a benign pattern recorded as a false positive stops producing the same finding. Accuracy improves as a function of use rather than of rule maintenance, and the customer’s own environment defines what counts as normal within it.
Pre-investigated detections
Identity detections are pre-investigated before they reach a human. The AI-SecOps Autonomous Analysts gather the evidence an analyst would have gathered, namely the account’s baseline, its recent access history, the privilege it holds and the state of every host and domain in the event path, and then either escalate with a written rationale or close as benign with the same rationale recorded for audit. That reduces analyst burden rather than merely alert volume: suppression discards events that might have mattered, pre-investigation removes the reconstruction work instead.
In action: impossible travel and business email compromise
Problem
A finance manager signs in at nine in the morning, having entered credentials into a phishing page the previous evening. Five minutes later a threat actor uses the same credentials to authenticate from another continent. The construction is illustrative rather than a customer incident.
Mechanism and outcome
The authentication anomaly registers a physical impossibility, and behavioral deviation concurs, because the source address and device are absent from the account’s history. The engine corroborates against DNS Shield, which blocked the phishing domain resolved the previous evening, and against Attack Surface Monitoring, which had flagged the address in credential-exposure intelligence. Four signals concur, the score reaches the Critical band, and the playbook suspends the account and revokes its sessions within seconds.
Attackers no longer break in. They log in.
Response acts at the identity: disable, revoke, reset and step up, with a complete audit record.
Request a Demo