
Trusted by security teams and service providers
When tools work in silos, your team must connect the dots
Separate tools generate alerts, apply different priorities and hold different parts of the evidence. Analysts must work out which events belong together, reconstruct the incident and coordinate a response.
That manual work adds operational complexity and cost.
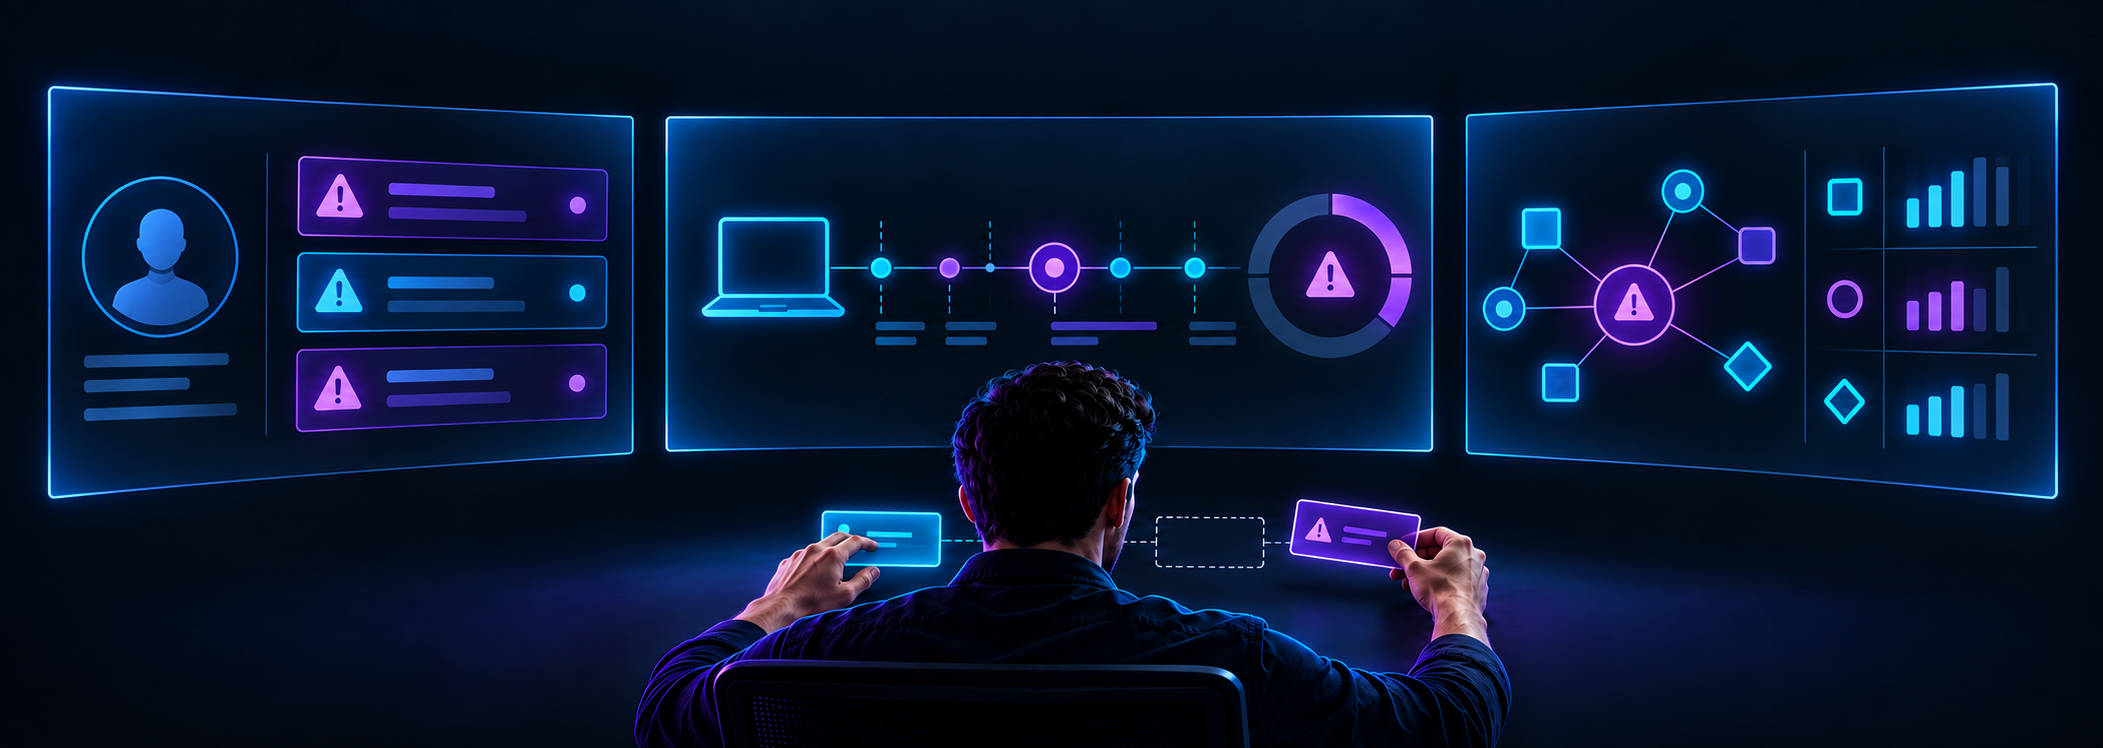
Disconnected tools. Fragmented context.
Each tool has its own data model, severity logic and console, leaving analysts to reconcile the information.
More alerts. Missing connections.
Alerts arrive separately, leaving analysts to determine how they relate before deciding what to do.
Lack of cross-layer visibility
An attack can span identity, endpoint, DNS and external exposure. When each tool sees only its own layer, analysts cannot see how those signals connect.
Manual work with a growing cost.
Manual correlation, custom integrations, per-tool tuning and duplicated licensing add to the cost of security operations.
Intelligent and integrated
security operations in one platform
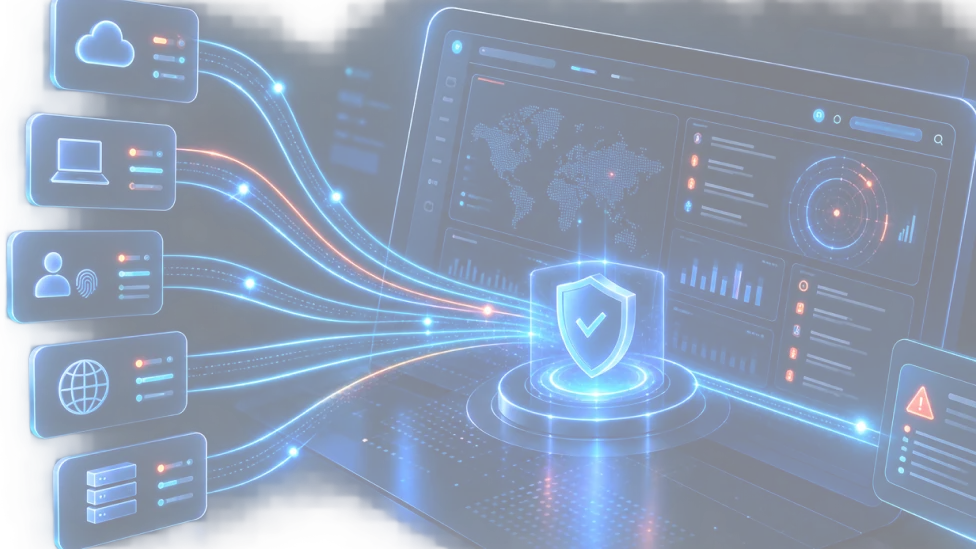
ClearSkies iISOC brings threat detection, investigation and response into a shared operating environment. Intelligence connects the evidence; integration enables capabilities to work together.

Intelligent
Connect the signals and understand the threat.The iCollector normalizes supported telemetry, and the Centric-AI Fabric enriches it and links related entities. The TDIR engine applies AI and machine learning to detect threats and correlate events into incidents, with MITRE ATT&CK context to support investigation.
Integrated
Bring your capabilities into one operating environment.Core capabilities, enabled native add-ons and supported third-party telemetry contribute to the same platform. Integration is built into its architecture, giving analysts shared context for investigation and coordinated response.
Why intelligence and integration need each other
Bring supported telemetry into a common model. Shared users, devices and domains connect activity across security layers.
Investigate related evidence, prioritize incidents and coordinate response under configured approval rules.
Review incidents, investigation evidence, response activity and operational reporting within the same platform.

One Platform.
One Workflow.
One Console.
ClearSkies iISOC coordinates its capabilities within a shared operating environment, bringing related security activity into one analyst workflow. Your team can investigate connected evidence and coordinate response across supported controls from one console, reducing the manual work of piecing findings together across separate tools.
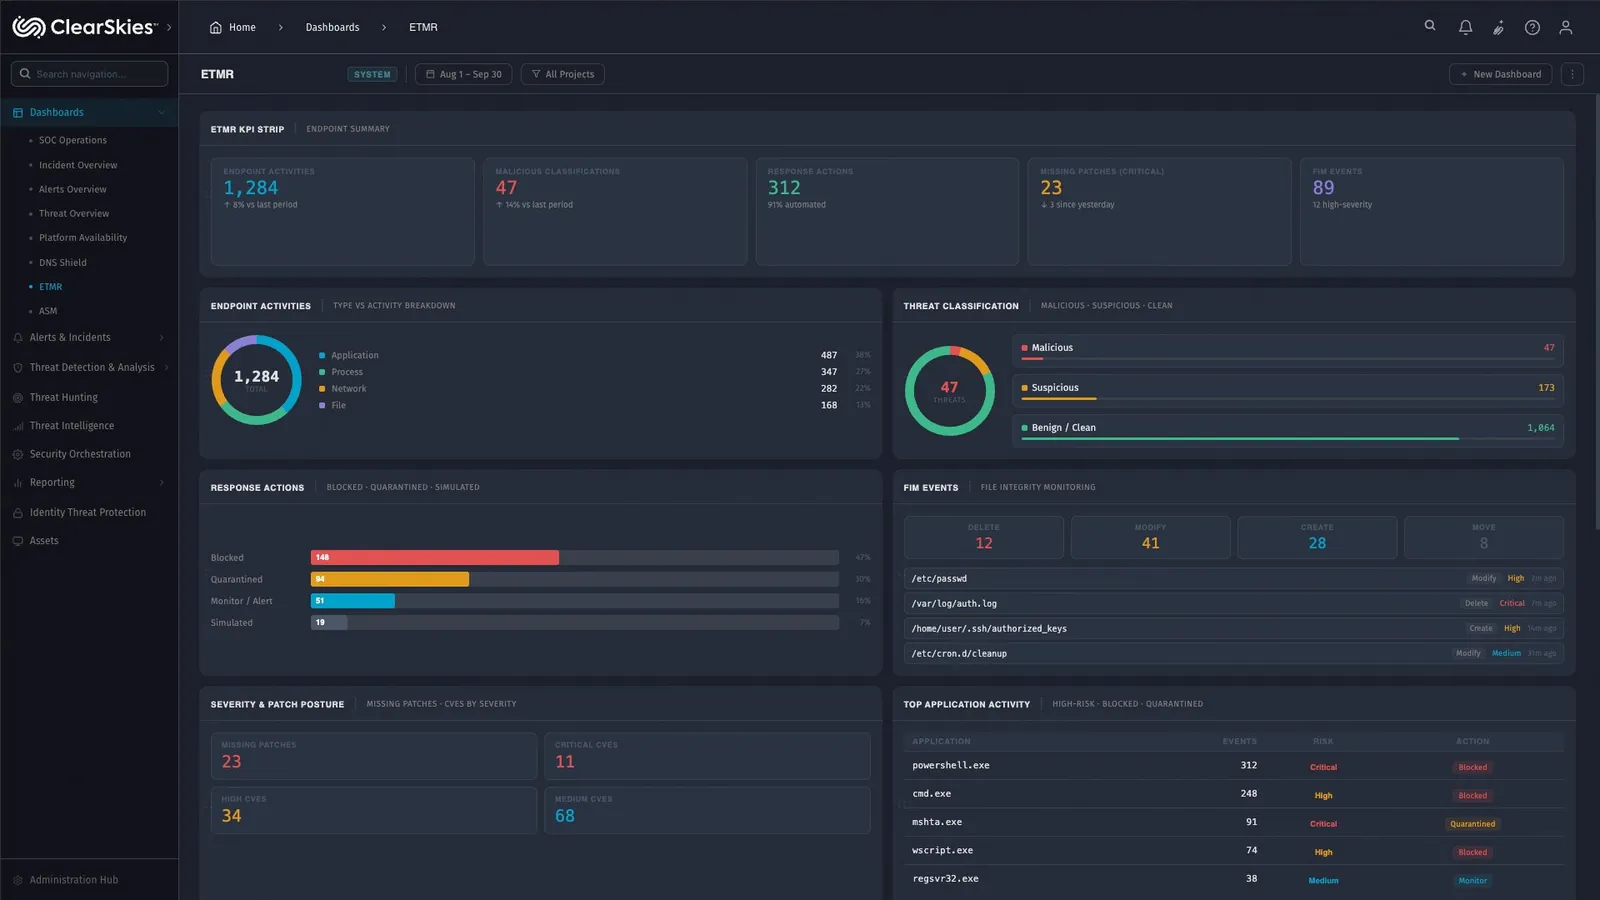
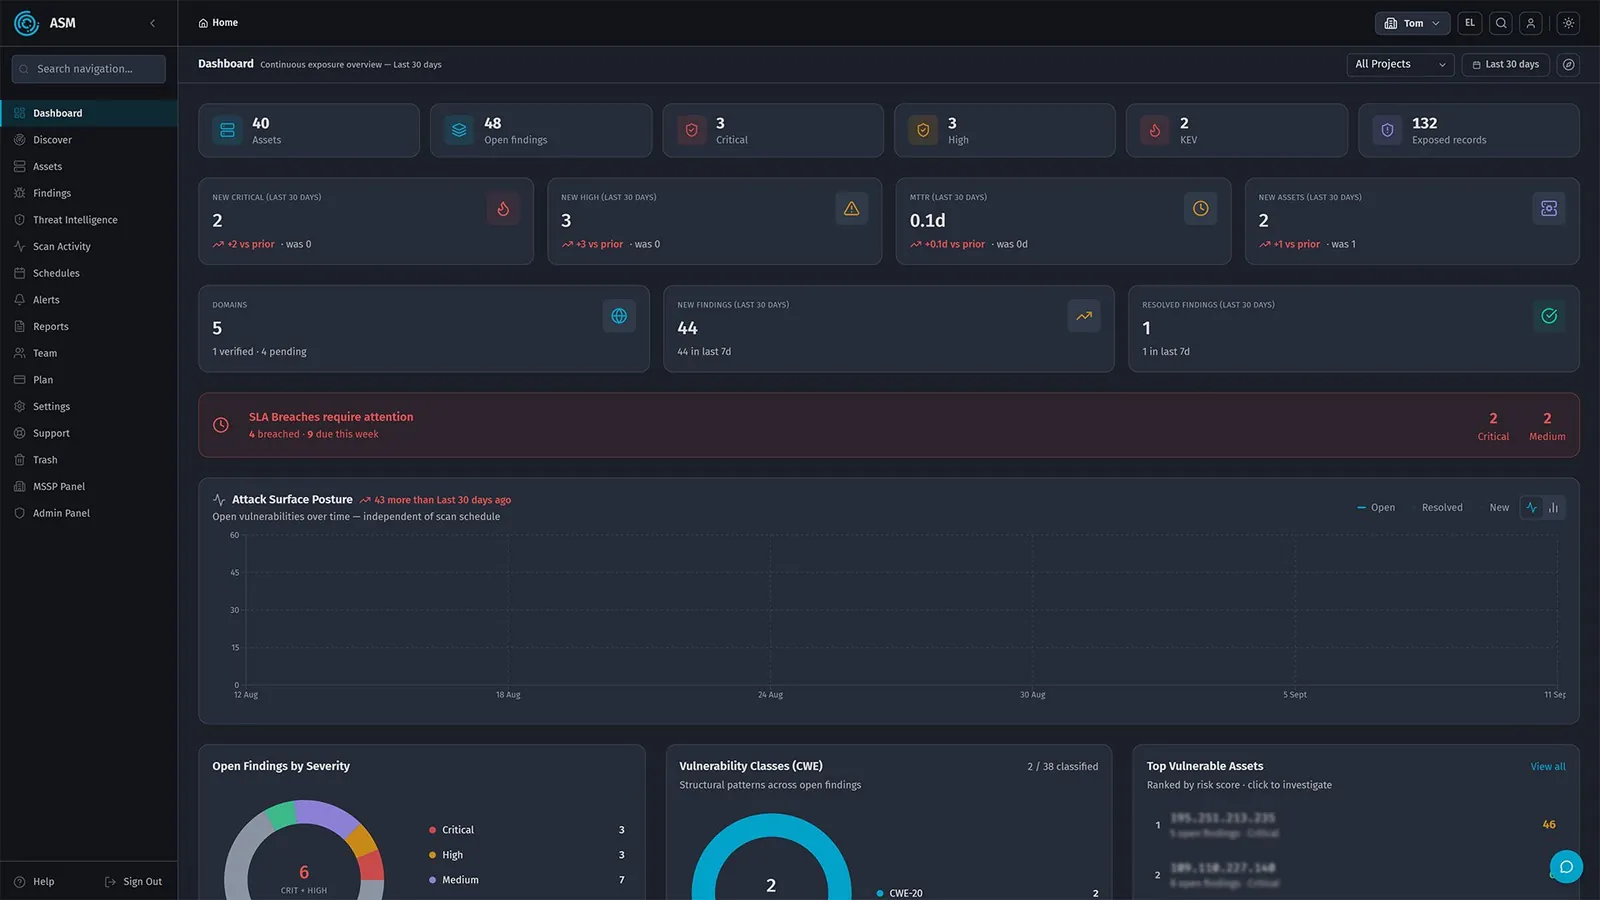
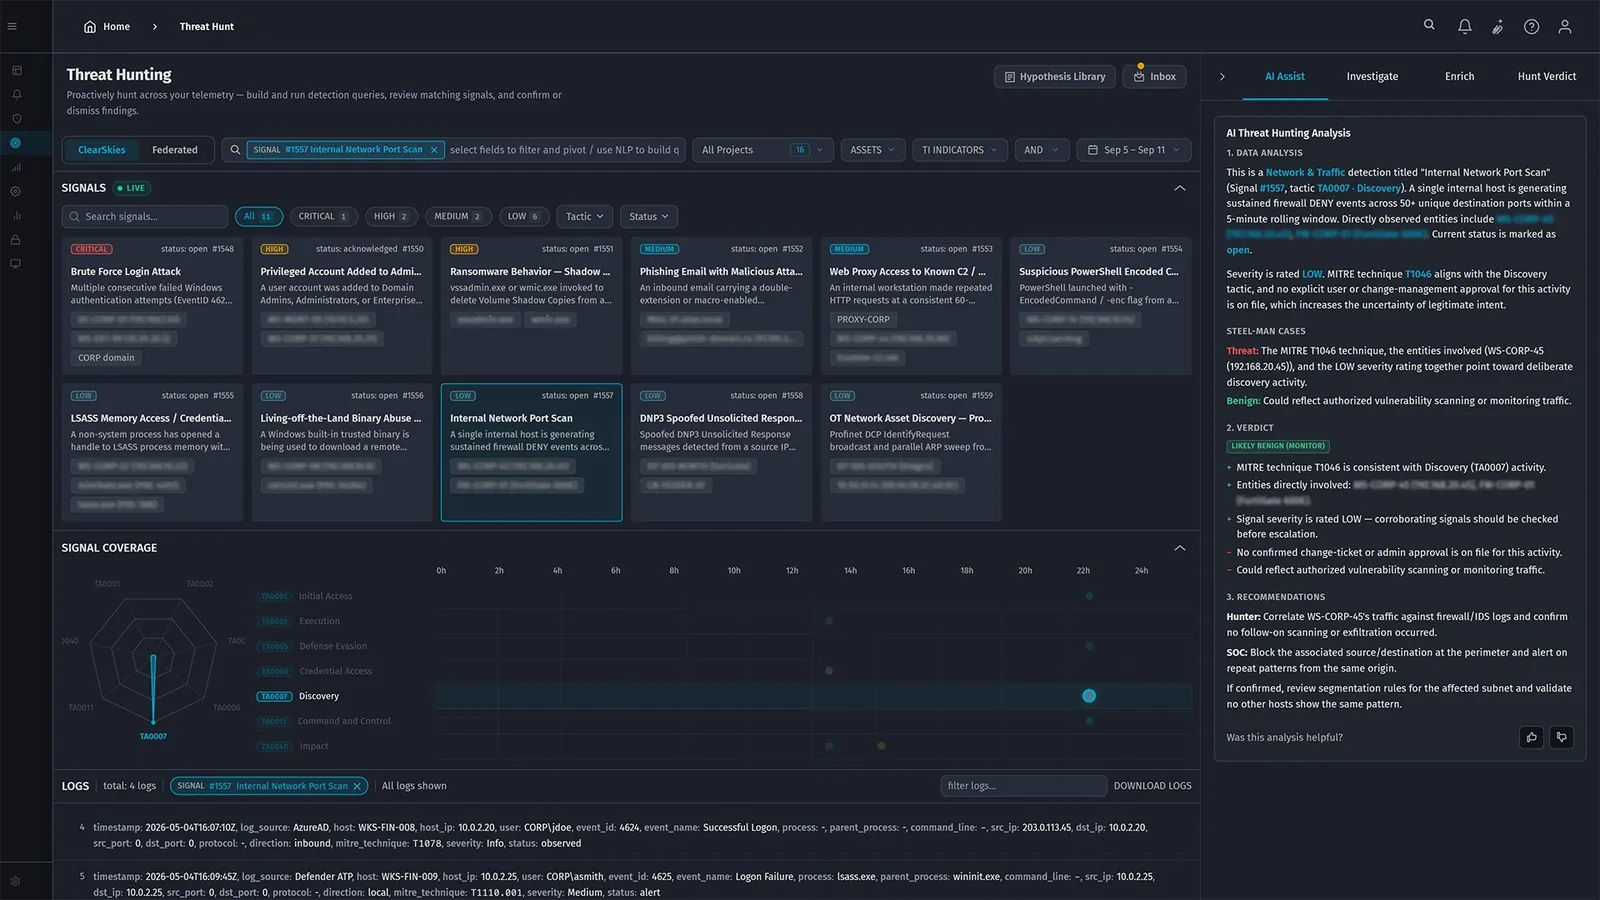
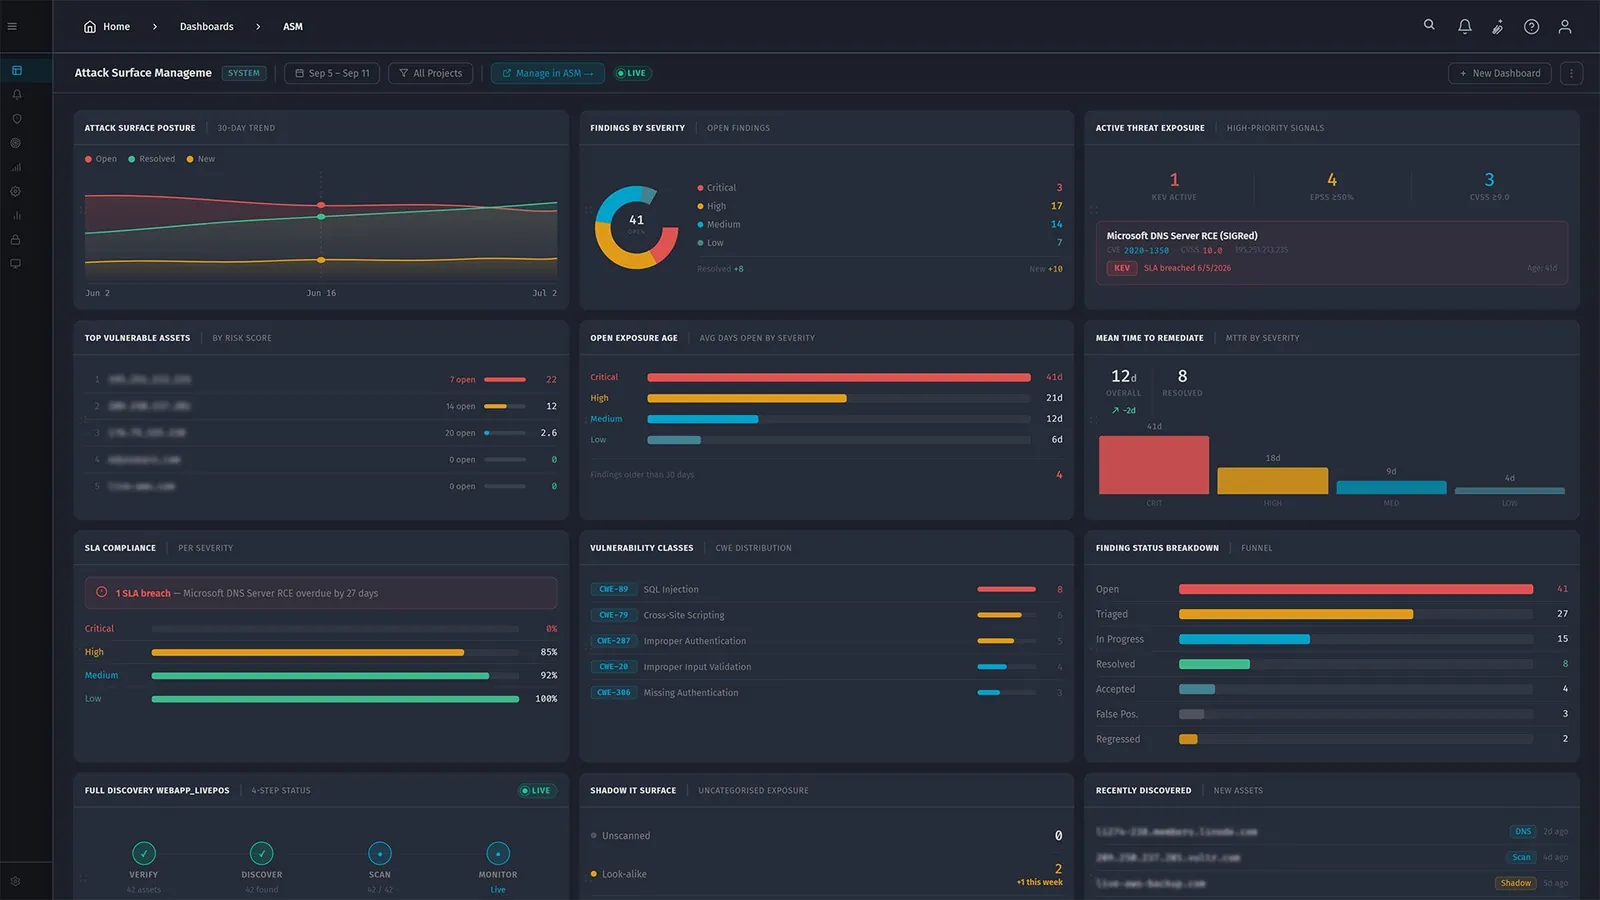
Extend coverage without adding a console.
Six native add-ons extend coverage across the attack surface. Each activates per tenant and is licensed on the unit that reflects its actual protected surface , so cost tracks what you're protecting, not what you're ingesting.
Attack Surface Monitoring
Finds what's exposed on your perimeter before an attacker does, continuously
DNS Shield
Blocks malicious destinations at the DNS layer, before a connection is made
Identity Threat Protection
Detects credential abuse and identity attacks across human and service accounts
Endpoint Threat Monitoring & Response
Detection and response on the endpoint, correlated with everything else the platform sees
Active Defense
Deception and containment that engages an attacker already inside
AI-SecOps Autonomous Analyst
Triages and investigates alerts autonomously, with reasoning your analysts can inspect
Outcomes you can trace,
not figures you have to trust.
Fewer False Positives
Related events resolve into single incidents inside the normalized model, and risk scoring with per-detection tuning directs what is created rather than what is received.
Reduce alert fatigue
Less investigation time
Automation and AI-enriched context multiply scarce security talent
Enhance efficiency & operational effectiveness
Higher analyst productivity
One workflow and one console, with volume triage absorbed by the Autonomous Analyst under governed authority.
Contain threats sooner and reduce impact
Run It In-House, Or Deliver It As A Service
The same platform, from one common core, packaged two ways - so it fits how you operate, whether you protect one organisation or hundreds.

Enterprise
Your analysts investigate one incident instead of reconciling a dozen alerts, because the reconciliation already happened in the data model. Response is orchestrated across your controls rather than executed tool by tool. Mean time to detect and mean time to respond fall, and the platform produces the auditable record that proves it. When you extend coverage, you add capability, not another console for your team to run.
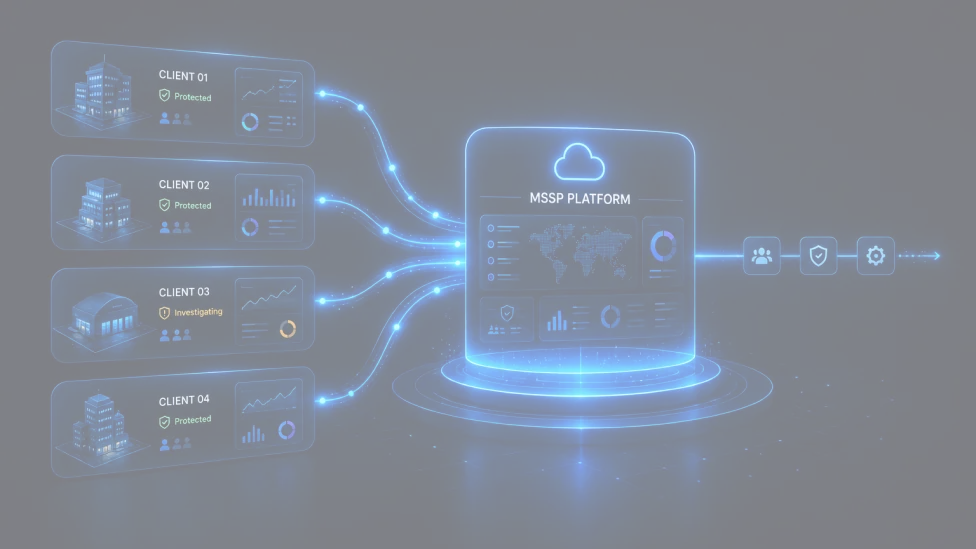
Service Provider
One multi-tenant platform serves the whole book of business through a single analyst workflow and a branded client portal, with strict per-tenant isolation and federated learning that improves detection for every tenant simultaneously. Because measurement is native, the provider reports outcomes rather than activity. Because capability is unified, new clients and integrations onboard without a bespoke build each time.
Organizations trust ClearSkies™
to stay ahead of tomorrow’s threats
“The multi-tenant architecture of ClearSkies™ makes client management effortless. We gain unified visibility across all customer environments while ensuring strict data segregation and compliance.”
See Across Every Layer.Contain Every Threat.
The same platform, from one common core, packaged two ways - so it fits how you operate, whether you protect one organisation or hundreds.
Recognized in the industry
Gartner® Magic Quadrant™ for SIEM, 2021 & 2024
Odyssey Consultants Ltd. was positioned as a Niche Player for the ClearSkies TDIR in 2021 and 2024, marking ClearSkies’ second consecutive inclusion in this Magic Quadrant
Gartner® Peer Insights™
ClearSkies Cloud SIEM rated 4.7 out of 5, from verified reviews in the Security Information and Event Management market.